The update
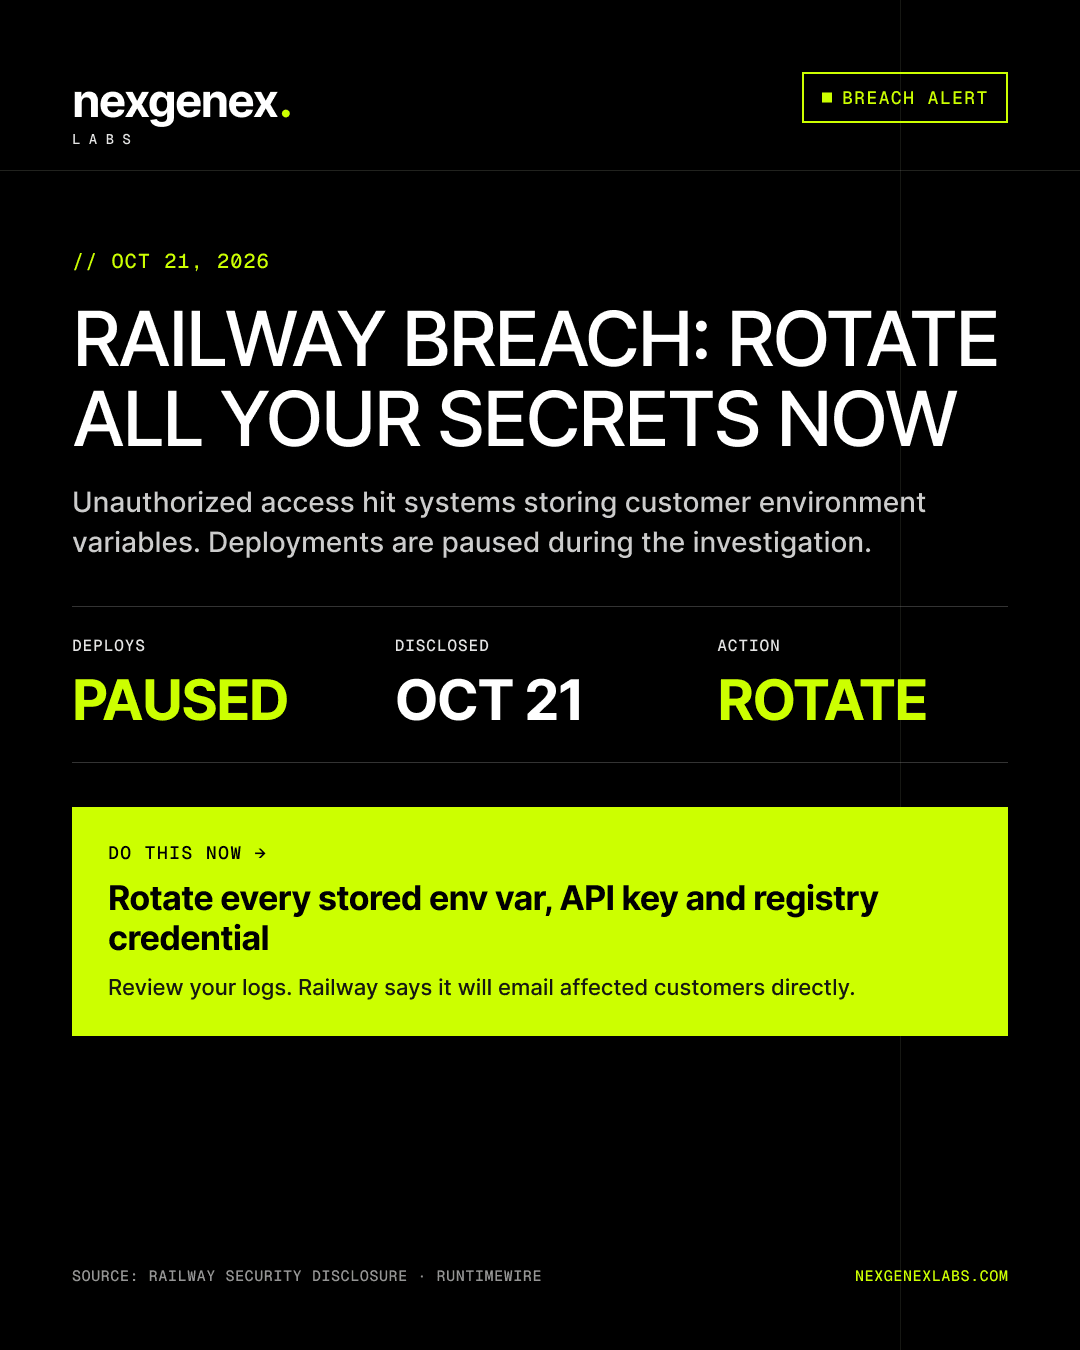
On October 21, 2026, Railway said it detected anomalous activity in systems that store customer environment variables. An unauthorized party may have accessed encrypted variables and, for some, obtained the decrypted contents.
Key facts
- Exposed values may include API keys and database or registry credentials.
- Impact may be limited to a subset of users, but affected accounts have not been named; Railway will email them directly.
- All deployments are paused during the investigation.
- Railway links the incident to recent attacks on platform companies aimed at AI inference providers.
What to do now
Rotate every secret stored on Railway at the provider, not just in the dashboard, then check provider logs for misuse. Our step-by-step rotation checklist covers the order to work in.
Sources
Have a project like this in mind?
Talk To Our Team →